24/7 SOC with MDR and XDR for companies in Mexico.
A team of analysts monitors your environment, investigates every signal and executes authorized responses to real threats. XDR correlates endpoint, network, identity and cloud; MDR turns that visibility into containment and continuous follow-up.
What is a 24/7 SOC with MDR and XDR?
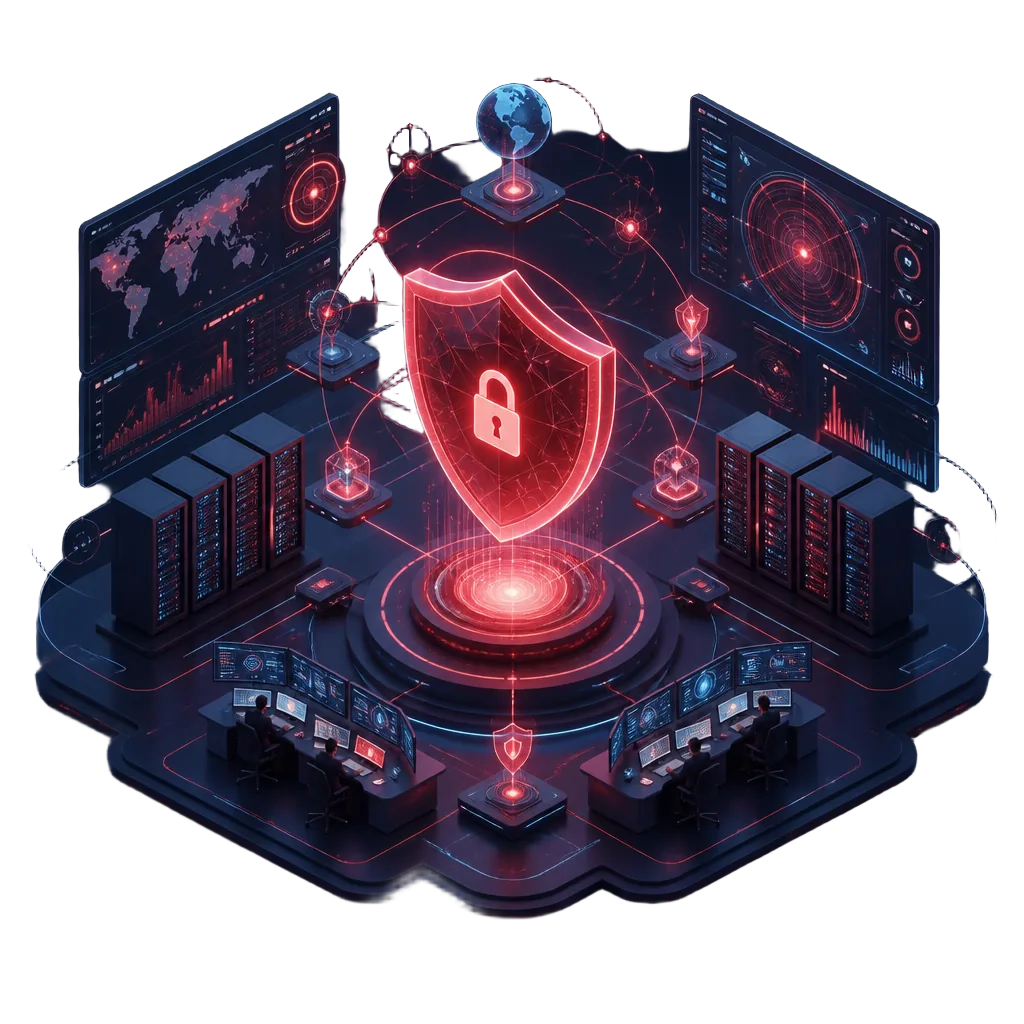
A 24/7 SOC is a security team that continuously monitors, investigates and responds to incidents. MDR is the managed service that delivers detection and response; XDR is the platform correlating endpoint, network, identity and cloud signals to accelerate containment.
This page covers security. If the same team must also operate availability, infrastructure and network changes, explore SNOCaaS. See unified SOC + NOC operations
How the BITS 24/7 SOC operates
Every signal moves through four stages: monitoring, detection, human validation and response. Your team receives prioritized incidents and clear actions, not another queue of alerts.
24/7 Monitoring
Continuous oversight of networks, endpoints, identities and cloud to find anomalies and suspicious activity.
Threat Detection
XDR correlates telemetry and behavior to detect threats that isolated tools cannot see.
Analysis & Validation
Security analysts remove false positives, reconstruct the attack and determine its real risk.
Response & Recovery
Using agreed playbooks, we isolate devices, block access and document incident recovery.
Detection is not enough: respond before impact
The service combines continuous coverage, specialists and response controls to reduce exposure without adding workload to your team.
Reduced exposure time
Drastically shrinks the time an attacker stays hidden in your network. Our analysts detect and contain threats before they escalate.
- Proactive 24/7 detection
- Automated containment
- Continuous threat hunting
Specialized support without overhead
Avoid the burden and cost of building internal shifts. Access a business-ready SOC with specialized analysts from day one.
- No hiring or training
- Immediate scalability
- Executive reporting
Protected operational continuity
Reduce downtime risk from ransomware, credential theft and targeted attacks through coordinated containment and evidence-led recovery.
- Incident response
- Documented recovery
- Regulatory compliance
In-house SOC, managed SIEM, EDR, MDR and XDR: what each model covers
Most companies don't need more alerts — they need someone to close them. Here is how the models on the market compare.
| Model | What it covers | Where it falls short |
|---|---|---|
| In-house SOC | Monitoring with your own staff, tools and business knowledge. | True 24/7 coverage needs 6 to 8 analysts on shifts, plus years of process maturity. |
| Managed SIEM | Log collection, normalization and correlation with alerting rules. | It delivers alerts, not containment: your team still investigates and responds. |
| Managed EDR | Detection and containment on endpoints and servers. | No visibility into network, identity or cloud: attacks starting in email or SaaS slip through. |
| BITS MDR | AI detection, human validation and response executed 24/7 with authorized playbooks. | Requires defining, in writing, the containment scope allowed in your environment. |
| BITS XDR | One case correlating endpoint, network, identity and cloud, already prioritized. | Needs source integration: 1 to 2 weeks of onboarding before active detection. |
BITS can operate MDR and XDR as a specialized security service. When you also need NOC and infrastructure operations under one watch, SNOCaaS is the right model.
Why detection time defines the cost of an incident
Global average to identify and contain a breach
IBM Cost of a Data Breach Report 2024
Containment target for P1 incidents in the BITS SOC
BITS contractual SLA by severity
Analysts on shift operating from Chihuahua
BITS operations center
Layers that strengthen your 24/7 SOC
Security monitoring gains context when connected to endpoints, identities, vulnerabilities, cloud and industrial environments.

Step inside our 24/7 SOC.
We'll show you live how our analysts detect, validate and contain threats — using your own use case on the table.
- Guided 30-minute tour
- No commitment or cost
- Real use case with your stack
- Executive report delivered
Operations protected 24/7 by BITS
Companies across Chihuahua and Mexico that trust our SOC for monitoring, detection and response.
Paseo Central – Chihuahua
Integración tecnológica para un complejo comercial, hotelero y corporativo.
- CCTV Digital IP de Misión Crítica
- Control de Acceso Avanzado
Grupo México
Seguridad y automatización para ambientes mineros exigentes.
- Monitoreo Integral con IA
- Reducción de Costos en Operación
Grupo Bafar
Servicios Administrados de red LAN/WAN y Seguridad Perimetral.
- Disponibilidad histórica documentada del 99.13%
- Optimización histórica de costos WAN
Partners y tecnologías que dominamos
More on Managed Detection & Response
Curated articles from our blog on 24/7 security operations, threat hunting and incident response.
Frequently asked questions
Your network never sleeps. Neither do we.
Schedule a 45-minute security assessment. We evaluate your current posture, identify critical gaps and design a 24/7 protection plan tailored to you.
NDA available subject to signature · For C-Level and IT Directors