Stop the attack before it spreads.
24/7 monitoring, analysis and response across servers, endpoints and mobile devices. FortiGuard experts filter alerts and we operate the response so your team can focus on what's strategic.
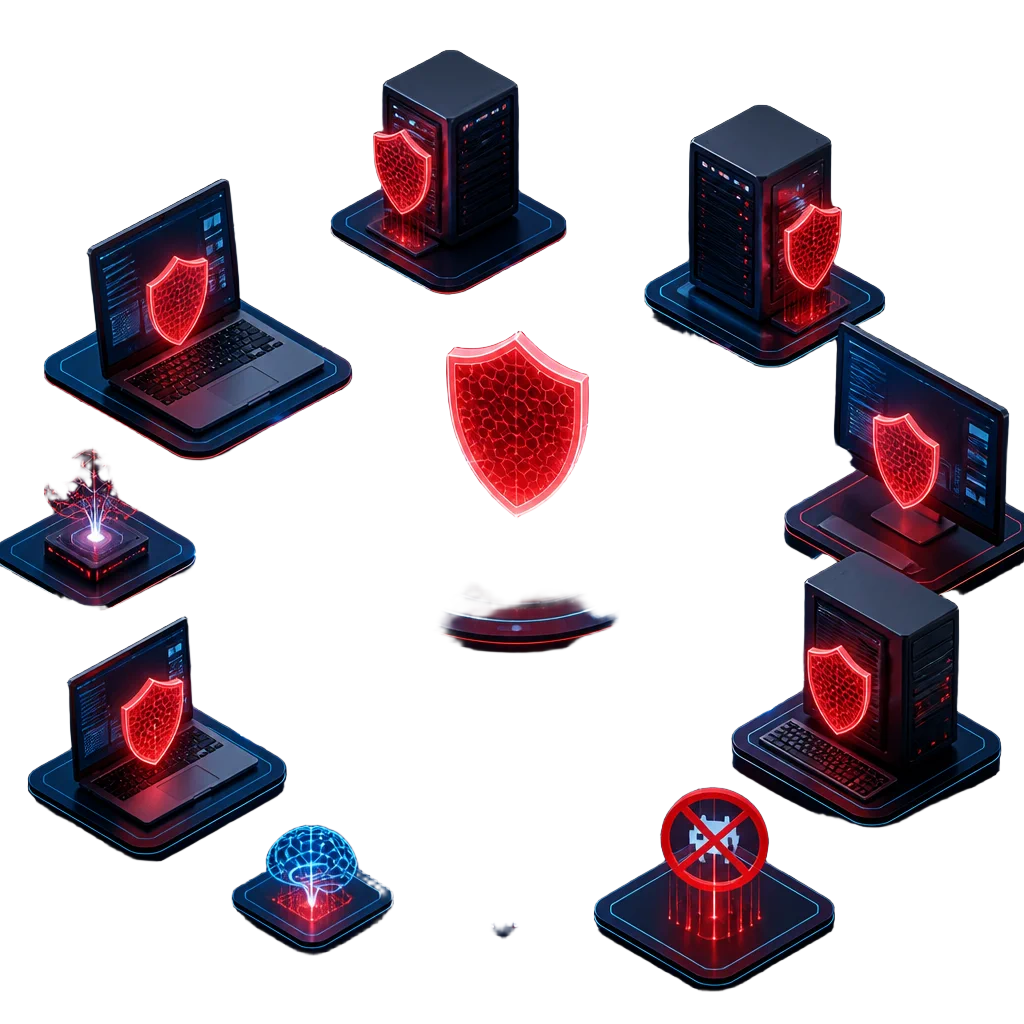
Traditional antivirus no longer stops the modern attack
Ransomware and fileless attacks bypass signatures. Without behavioral detection and expert response, the minutes between intrusion and encryption are your only defense.
Alert fatigue
Your IT team drowning in false positives loses sight of the real, critical incidents.
No in-house 24/7 SOC
Attacks don't respect business hours. Without nightly and weekend monitoring, the impact window is enormous.
Managed EDR by BITS + FortiGuard
Automated real-time defusion, risk-based triage and expert-operated response under the agreed policy, coverage and service scope.
FortiEDR · key capabilities
Detection
Defusion
Surface
Legacy
Six capabilities that turn FortiEDR into a 24/7 MDR service
Technology detects; the service contains. This is how BITS operates Fortinet's EDR alongside FortiGuard analysts.
Real-time detection and defusion
Applies automated containment during an attack according to policy, agent coverage and threat type.
- Policy-based containment
- Behavioral analysis
- Anti-ransomware
24/7 monitoring by FortiGuard MDR
Fortinet experts perform triage and response based on your company's risk to prioritize actionable alerts for your team.
- Expert triage
- Risk-based response
- Night and weekend coverage
Attack surface reduction
Control unmanaged devices, identify vulnerable IoT and apply policies before threats find a way in.
- Device discovery
- USB and peripheral control
- Endpoint hygiene
Security Fabric integration
Share intelligence with firewalls, email, identity and SIEM for automated responses across the entire stack.
- FortiGate, FortiMail, FortiSIEM
- SOAR as a service
- Shared context
Legacy system protection
Virtual patching to protect old servers, medical equipment and OT without official vendor patches.
- Windows EoL
- Medical equipment / OT
- No reboots or changes
Automated and assisted response
Ready-to-use playbooks to isolate hosts, kill processes, roll back changes and leave forensic evidence for audit.
- Automatic isolation
- Change rollback
- Forensic evidence
Do you know how long it takes your team today to contain ransomware?
30-minute session with a BITS architect. We review your endpoint estate, your current coverage and the gaps versus a 24/7 MDR.
- Fast endpoint inventory
- 24/7 coverage analysis
- Current MTTR estimate
- No cost, no commitment

Does your team operate the EDR, or does the EDR operate against your team?
Technology alone is not enough. The difference is who operates it, with what experience, and at what hour of the day.
Self-managed EDR
- MonitoringYour team (8/5 or 24/7)
- WorkloadHigh · alert fatigue
- ExpertiseRequires in-house analysts
- ResponseYou run the playbooks
Managed EDR (MDR)
- MonitoringExternal experts 24/7
- WorkloadMinimal · only critical alerts
- ExpertiseAccess to FortiGuard experts
- ResponseThe service helps and automates
Managed EDR is ideal if this sounds like you
You don't need more tools: you need someone to operate them with judgment, around the clock and with a measurable SLA.
- You don't have an in-house 24/7 SOC.
- Your IT team suffers alert fatigue from false positives.
- You manage critical environments: OT, critical servers, points of sale.
- You need evidence for compliance (PCI DSS, HIPAA, ISO 27001).
- You want to reduce the total cost of security operations.
Kill chain · MDR response
Initial access
Execution
Lateral movement
Impact
From deployment to verified containment
A clear four-step cycle, operated by BITS and FortiGuard, so your team can focus on what's strategic.
Deployment
We install FortiEDR agents on servers, endpoints and mobile devices. We tune policies to your operation.
Tuning and baseline
We calibrate detections, define critical assets and reduce false positives before go-live.
24/7 operation
FortiGuard MDR monitors and triages, and BITS coordinates response and communication with your team.
Continuous improvement
Monthly reports, lessons learned and playbook adjustments. Your posture improves every month.
More than detection: benefits for the whole business
Managed EDR not only protects you: it helps you comply, save and continuously improve your security posture.
Regulatory compliance
PCI DSS, HIPAA, GDPR and ISO 27001 require active endpoint monitoring. We deliver audit-ready evidence.
Cost reduction
Preventing a breach is significantly cheaper than recovering from a ransomware attack or paying a ransom.
Continuous posture improvement
FortiGuard's learning about global threats improves your local defenses every day, with no extra work from your team.
EDR becomes more powerful with the rest of the BITS stack
Combine it with our services to cover every layer of your operation, from endpoint to cloud.
Vulnerability management
Continuous discovery and prioritization by real risk to close the door before the attack.
Threat advisory
Actionable intelligence on active campaigns to prevent incidents before they escalate.
Network security
Firewalls, segmentation and NDR integrated into the Security Fabric for end-to-end visibility.
Identity and cloud
Granular permissions and access controls for users and cloud workloads.
SOC / SIEM / SOAR
Correlated events, automated playbooks and orchestrated response across your entire surface.
GRC
Governance, risk and compliance to reduce the regulatory impact of any event.
Why run your EDR with BITS
Fortinet technology, FortiGuard intelligence and a local team that responds with names, not tickets.
Integrated Fortinet platform
FortiEDR native to the Security Fabric, not just another agent to manage.
FortiGuard intelligence
Global telemetry with advanced analytics and machine learning applied to your environment.
SOAR automation
Orchestrated response with playbooks ready for the most critical scenarios.
Service managed by BITS
Local team in Chihuahua coordinating with FortiGuard 24/7. A single point of contact.
Frequently asked questions
Managed EDR and response scenarios
Explore references for assessing coverage, triage and response with FortiEDR + FortiGuard MDR. Scope and results are validated for each operation.
Paseo Central – Chihuahua
Integración tecnológica para un complejo comercial, hotelero y corporativo.
- CCTV Digital IP de Misión Crítica
- Control de Acceso Avanzado
Grupo México
Seguridad y automatización para ambientes mineros exigentes.
- Monitoreo Integral con IA
- Reducción de Costos en Operación
Grupo Bafar
Servicios Administrados de red LAN/WAN y Seguridad Perimetral.
- Disponibilidad histórica documentada del 99.13%
- Optimización histórica de costos WAN
Partners y tecnologías que dominamos
More on EDR, ransomware and incident response
Hand-picked articles from our blog on endpoint threat detection, MDR and best practices in response.
Scope documented in the proposal
Coverage by eligible endpoint
Triage and response by scope
Objectives defined by contract
Related services and resources
Managed EDR is one layer. These pages explain how it connects with the rest of your security operation.
Ready for your endpoints to defend themselves, with experts behind them?
Book a 30-minute assessment. We review your endpoint surface, critical risks and design a Managed EDR plan tailored to you.